
Frame the decision
Name the audience, requested decision and source pack. Review imported tables and extracted text; record gaps instead of allowing a polished narrative to conceal them.
Draft a risk-and-issues brief from your business question and selected evidence. Organize proposed risks, likelihood and impact assumptions, open questions and mitigation options, then have the accountable risk owners review the sources and method before using the assessment.
An AI risk assessment generator can organize supplied risk material into a draft with proposed issues, assumptions and mitigation options. Business plans the question, audience and outline, attempts source-based number reconciliation where evidence is present, and surfaces bounded generated-draft Evidence and citation findings. It does not independently validate risk probabilities or impact estimates. Repair can retain original figures, citations need checking, and generation time depends on the inputs and review needed.
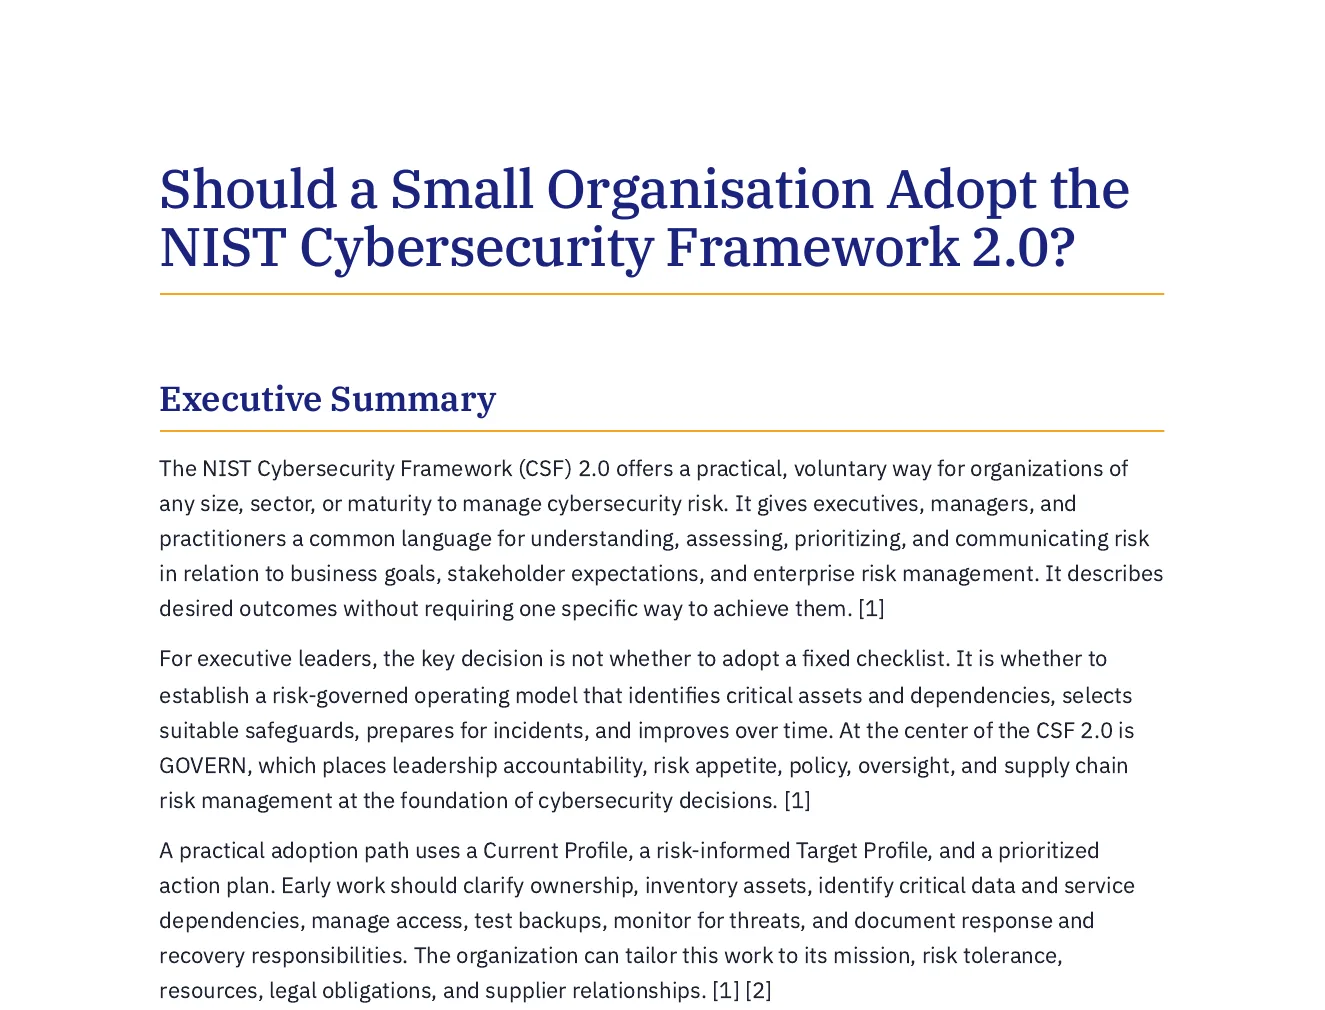
Inspect an actual Business report. A readable decision brief needs the question, supplied evidence, options, assumptions and next decision—not just a shorter source document.
Findings, options, risks and a recommendation, cited by number to two NIST publications.
Prepare an executive brief for the owner of a small organisation that holds customer information. It should say whether the organisation should adopt the NIST Cybersecurity Framework 2.0, what the framework's six functions ask of it, and what to do first. Use only the supplied documents and cite them.
Open the full export and compare its statements with the cited sources before reuse.
Name the audience, requested decision and source pack. Review imported tables and extracted text; record gaps instead of allowing a polished narrative to conceal them.
Separate supplied facts, calculated values, assumptions and recommendations. For variance work, reconcile the period, unit, baseline and actual value before interpreting the direction of a difference.
Use options, trade-offs, risks and named next actions. Review the final artifact and, when using Analyst calculations, inspect the calculation evidence separately from the narrative.
Select source documents, case context, working notes, assumptions, options and decision constraints before generation. Inspect claims, metrics, exact quotations, source tables and conflicting figures. Review decisions are scoped to the source or artifact and can become stale after evidence changes; unresolved evidence should stay visible.
Keep investment, recurring costs, benefits, delays, growth, discount assumptions and scenario probabilities explicit. Inspect deterministic cash flow and the available return, payback and sensitivity outputs. Compare scenarios before selection, and inspect the formula workbook or calculation receipt separately from the narrative recommendation.
Inspect the dossier's source tables, working rows and columns, calculation ledger and workbook handoff. Metric packs retain reviewable calculation and source context. Preview source replacements for a new period before accepting them. Execution records distinguish an action owner, baseline, target, measured value, data source and the reason for a status change.
A calculation can be replayable while the supplied inputs remain wrong. A generated report is decision support, not independent diligence, audit assurance or investment advice.
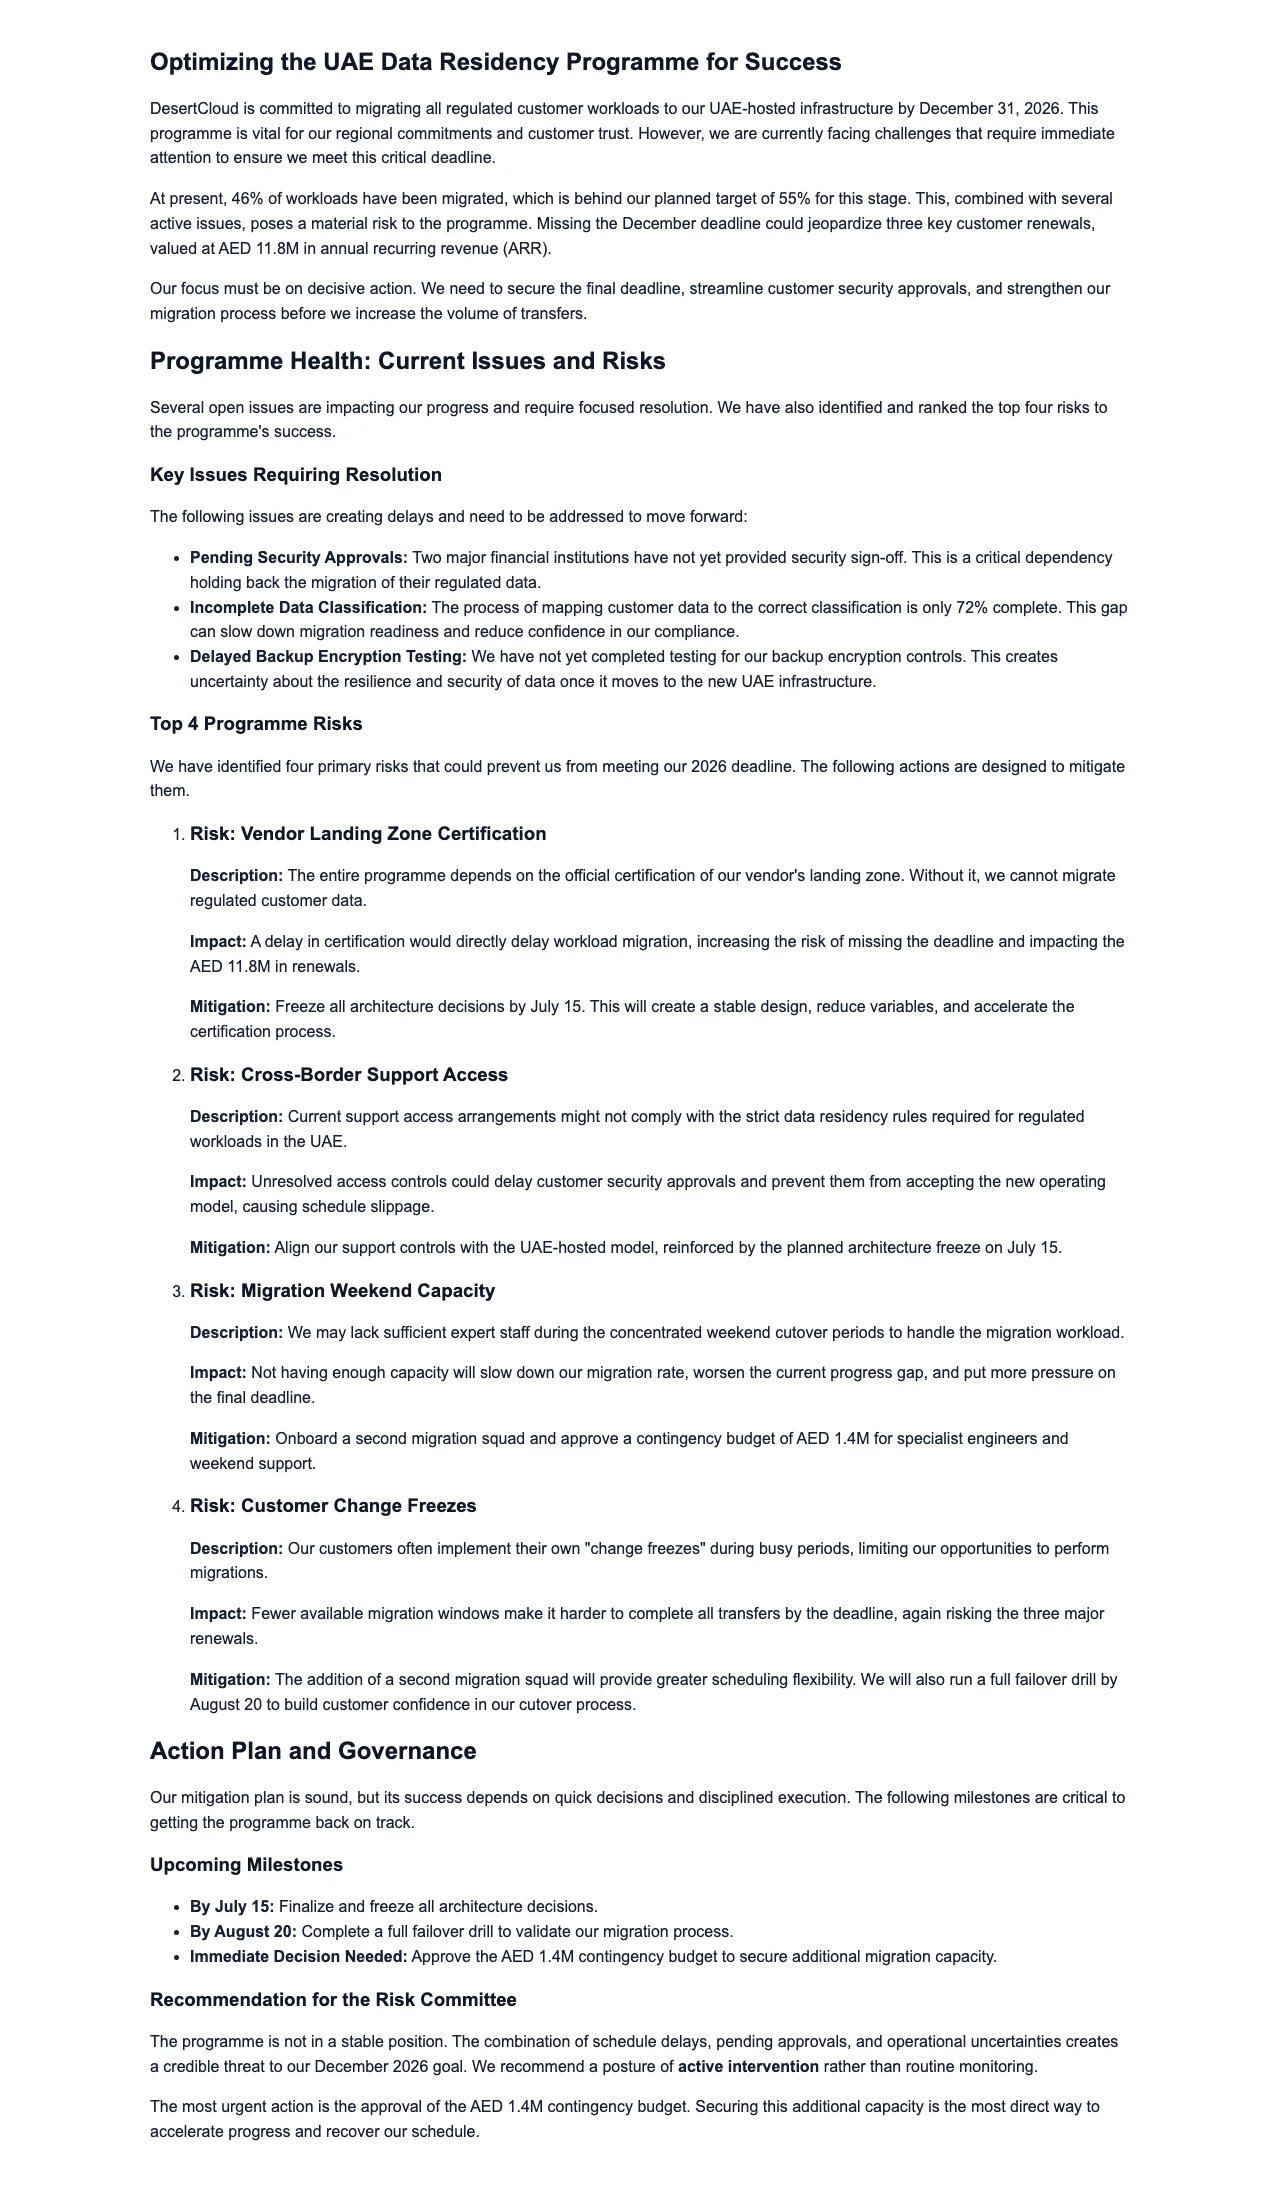
State the risk question, evidence scope and intended reviewer. Use the draft to organize proposed risks, assumptions, possible responses and missing information for accountable review.
Ask the draft to organize possible risks across the categories relevant to your business or project. Supply current records and review the proposed outline, missing evidence and issues the draft may have omitted. It does not establish that every material risk has been identified.
Supply the rating scale, period, likelihood assumptions and impact basis you want reviewed. Business can draft explanatory ratings and trade-offs, but number-token matching does not validate probability, loss estimates or the chosen risk method. Confirm each proposed rating and its source support with the accountable risk owner.
Ask for proposed preventive controls, contingency options, owners and follow-up checks. Edit them in supported Steps or Checklist blocks and verify that they address the actual exposure. Quick AI and Power Edit revise selected text; important changes need another source review. A draft can omit a needed mitigation or recommend an unsuitable one.
Provide the named rules, current records and scope you are authorized to use. Business can organize a regulatory-risk draft, apply supported Brand Dictionary terms and request uploaded-file citations. Review the references, interpretation and proposed response with qualified specialists; neither terminology checking nor a cited brief establishes compliance.
Supply the dated threat reports and control evidence relevant to the assessment. Check each material claim and citation against those sources; Business does not provide a continuously refreshed threat-intelligence feed. On Business Professional or higher, authorized security colleagues can comment on and review the saved draft.
Organize proposed risks, likelihood assumptions, impact basis, evidence and review notes in an editable comparison table. These ratings and statuses are authored brief content, not an automatically validated operational risk register. Check omissions and changed claims against the original records, then inspect the exported document before sharing it.
Describe the business context, project or decision and the risk question the reader needs answered. Attach dated evidence and identify any assumptions or unavailable records.
State the relevant categories in your request, such as operational, financial, regulatory, strategic, cybersecurity or supply chain. Review the proposed sections and evidence requirements before generating.
Business generates the draft from the reviewed outline and supplied sources. Source-based number repair is best effort and can leave original figures; citation markers remain model-generated. Inspect the generated-draft Evidence and citation findings, then validate the ratings, assumptions and proposed mitigations against the original material.
Edit with 20+ semantic blocks including Pros/Cons, KPIs, and Comparison Tables. Use Quick AI for instant rewrites or Power Edit for deeper revisions. On Business Professional or higher, comments and named sharing require an authorized content role. Review material risks and evidence, resolve save conflicts and confirm the final saved version before exporting.
Compare AI-generated risk assessments with traditional risk management approaches.
| Evaluation area | Gixo Business | What to check in an internal or advisory risk process |
|---|---|---|
| Assessment scope | Draft the risks, assumptions and proposed mitigations from the evidence you supply. | Check the agreed scope, risk method, specialist judgment and accountable risk owner. |
| Evidence review | Inspect generated-draft Evidence and citation findings and the original source material. | Confirm source dates, omitted risks and whether mitigations address the actual exposure. |
| Team review | Comments and named sharing require Business Professional or higher and an authorized current content role. | Test the review, version and approval workflow used by the responsible teams. |
| Delivery and timing | Revise the saved brief and resolve save conflicts before export; generation time depends on scope and inputs. | Compare the deliverable and responsibilities rather than assume a fixed assessment duration. |
Updated