
Make the intake specific
Supply the parties, document kind, jurisdiction, obligations, dates and reference material. Review imported content and retain its source identity before using it in a new matter.
Use Gixo Lex to prepare compliance documentation that keeps obligations, evidence notes, gaps, policies, working papers, and reviewer handoff in a structured artifact instead of a generic prompt answer.
Reviewed 2026
AI compliance documentation software is software that helps teams prepare, organize, and review compliance documents — checklists, evidence matrices, working papers, filing support notes, risk registers, and policy drafts — while keeping missing facts visible as gaps instead of asserting unsupported ones. Gixo Lex is this kind of tool: it can use your policies and source files to inform a reviewable draft, rather than returning a one-shot prompt answer. It does not watch controls, collect evidence automatically, or issue compliance signoff — final judgment stays with qualified reviewers.
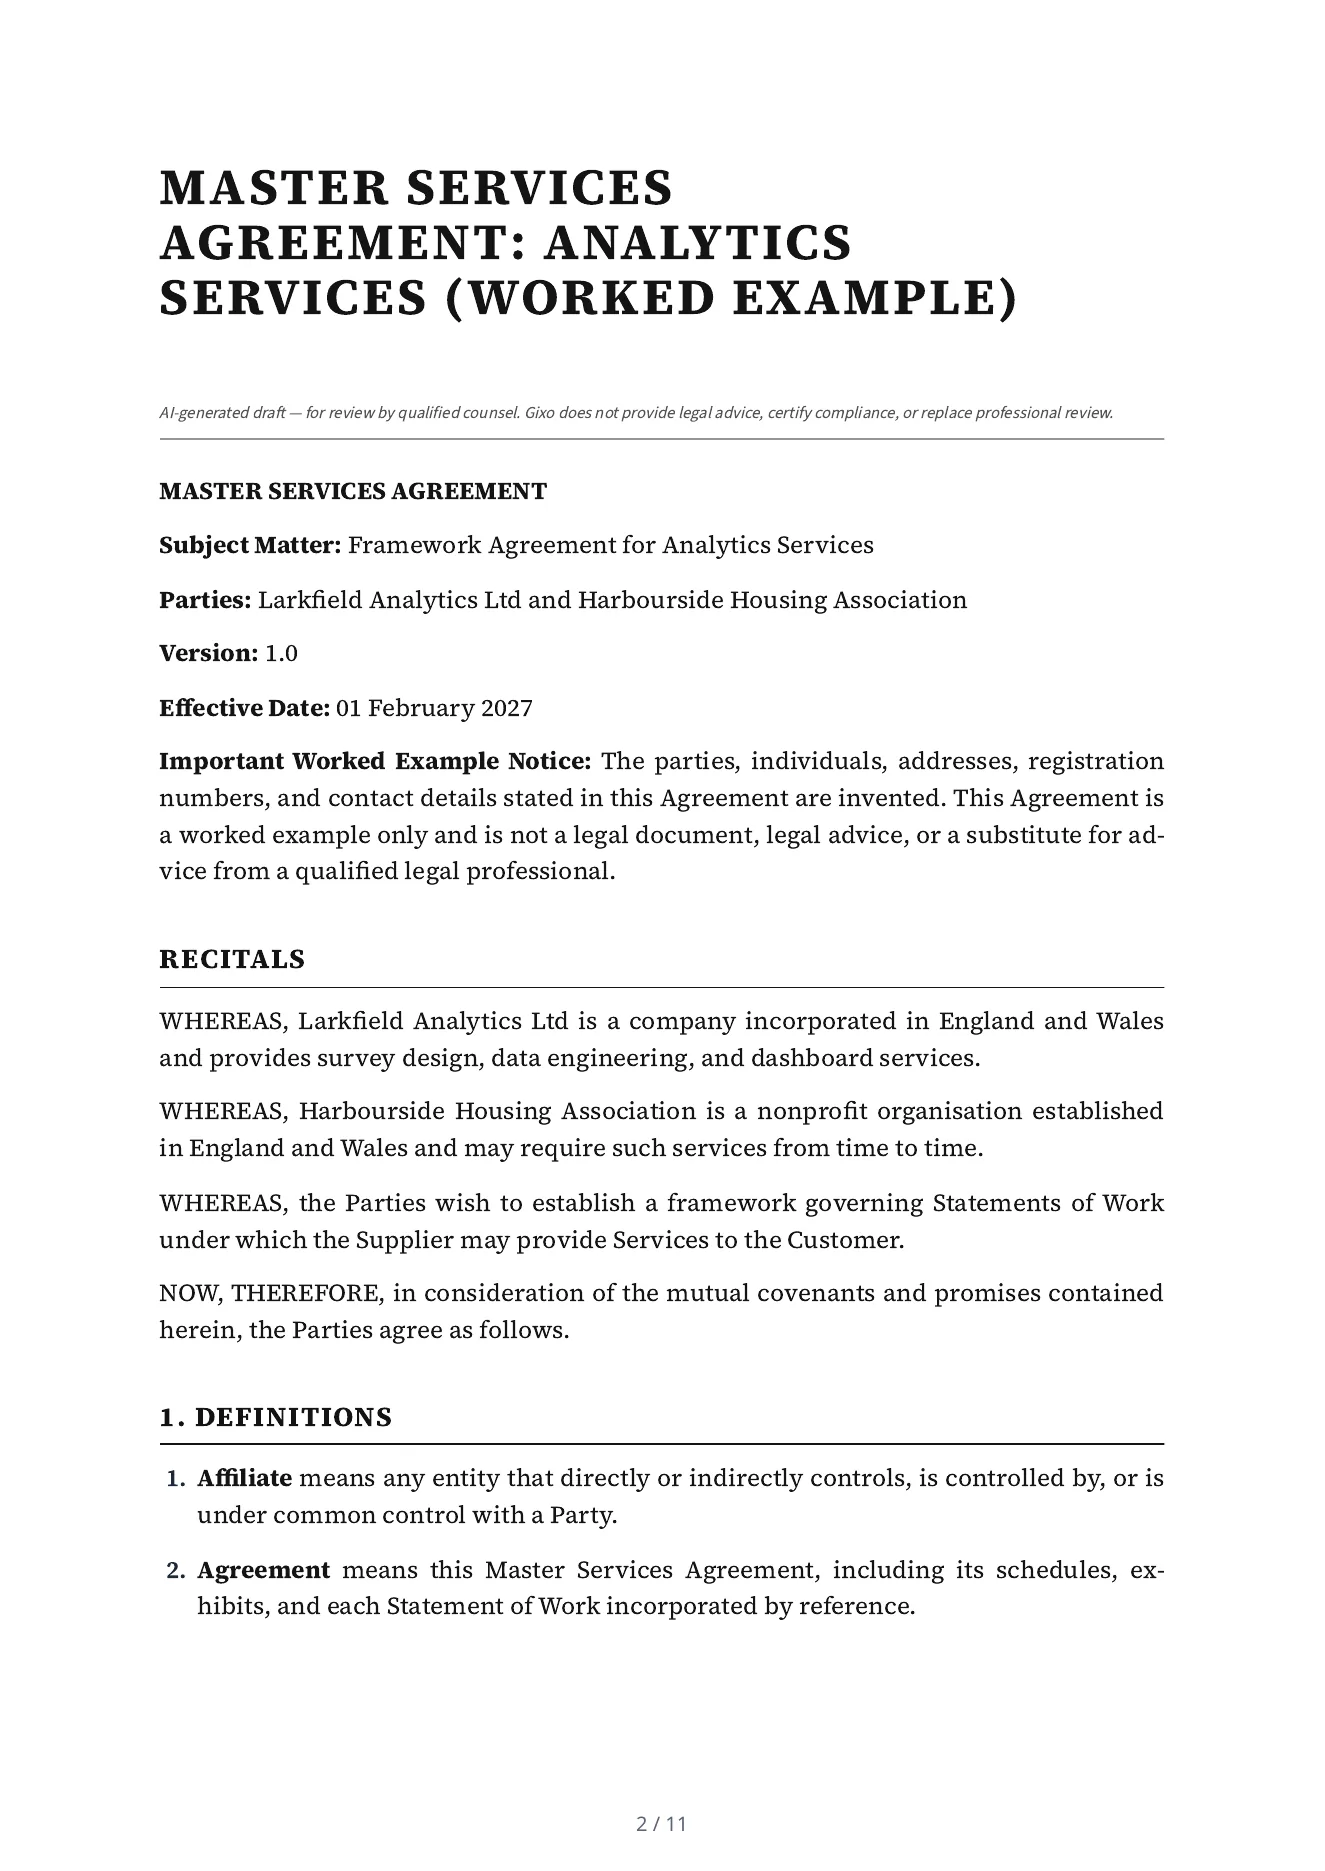
This is a real Lex export for invented parties. Inspect the input and clauses as a worked example, with professional review kept separate from automated drafting and checks.
A master services agreement of 17 numbered parts: definitions, scope of services, service levels and change orders, fees, intellectual property, confidentiality, data protection, warranties, indemnification, limitation of liability, force majeure, term and termination, transition assistance, governing law, general provisions and schedules. Its first page says it is a worked example, not a legal document.
Draft a Master Services Agreement: analytics services between Larkfield Analytics Ltd (Supplier) and Harbourside Housing Association (Customer). Governing law: England and Wales. Effective date: 2027-02-01. Term: Two years from the effective date, renewable by written agreement. Confidentiality: Five years after the agreement ends. The Supplier provides survey design, data engineering and dashboard services to the Customer under statements of work agreed in writing. Excluded: any service not set out in a signed statement of work. Dependencies: the Customer provides access to its systems and a named contact for each statement of work. State on the first page that the parties, people and addresses in this agreement are invented and that it is a worked example, not a legal document. The notice email address of Larkfield Analytics Ltd is notices@larkfield-analytics.example and of Harbourside Housing Association is notices@harbourside-housing.example (both invented).
Read mechanically against the intake, not by a lawyer: 10 of the 12 facts the intake gave are in the draft (the two registration numbers are not printed), nothing is left as a placeholder, and it states two terms the intake did not give, 30 days and 10 Business Days, which Lex chose.
Supply the parties, document kind, jurisdiction, obligations, dates and reference material. Review imported content and retain its source identity before using it in a new matter.
Use the legal workspace's permitted structural tools, Draft Checks and review paths. Compare proposed changes with the saved draft and original material; unsupported Word edits must be handled explicitly.
Have qualified counsel review enforceability, local requirements and the actual commercial intent. Check the current approval state and the downloaded document after a change.
Select the target clause and give Ask Lex a bounded instruction. Missing facts remain visible for review. Inspect the before-and-after proposal, required clause checks and any explicit outside-matrix or mandatory-clause override before versioned application. Use the legal workspace's structural allowlist rather than assuming every general content-editor block is available.
Inspect immutable playbook versions, anchored findings, provenance and precedent variants before staging a change. Matters retain original sources, quotation findings and source-version comparisons. Review extracted obligations for timing, ownership and source revision; negotiation turns and agreement-pack review cells have their own decisions and current-version requirements.
Original-format Word export, tracked changes against an original and saved-version redlines are separate paths. Unsupported edits must be surfaced rather than silently claimed as preserved. Inspect the layout, validator notes and downloaded file, then retain its delivery receipt. Counsel's review applies to the actual matter and version.
Every contract in Lex, drafted or imported, gets an AI contract review: each clause the document type expects marked present, weak or absent; up to 25 risks with a level, the party each falls on, why it matters and replacement wording; and provisions that cannot both be followed. Every quotation is checked against the contract text, findings are decided before approval, and there is no single risk score. The same review reads the key terms and obligations with the words they quote and proposes them into the Agreement Pack. Review every document puts up to 25 documents of an Agreement Pack, or up to 200 in a matter, into one table with your own questions as columns and an Excel export. Approvers can be named in order, and signing supports up to 10 signers with an optional signing order and automatic reminders; it is a simple electronic signature, not a qualified one. A qualified reviewer still decides what the contract says.
Lex does not provide legal advice or certify compliance. The public specimen is not a universally reusable legal template. Word fidelity depends on the supported original-document and saved-version path; unrestricted Power Edit and image insertion are not legal editing features.
Good compliance documentation software should help teams create a living set of reviewable work product without pretending that drafting equals signoff.
Connect the requirement, policy, control, evidence expectation, owner note, and open issue in the same document structure.
Reference files and governing context can shape the draft. Cited sources can show which draft sentences are supported by supplied reference files. This in-app support does not establish legal authority or statutory compliance and is not inserted into the contract or its exports; reviewers still check the facts and law independently. Missing facts remain placeholders or reviewer notes instead of asserted support.
Prepare checklists, evidence matrices, working papers, filing support notes, and policy drafts so the documentation package matches the review job.
Comments, review state, assignees, due dates, and versions stay attached to the same document, and each export is written to an audit log (who exported it, the format, and whether it succeeded) rather than stored with the document. This matters when legal, compliance, finance, audit, and operations all touch the same artifact.
A compliance document is dangerous when it reads final but hides unsupported claims. Gixo keeps the artifact in a reviewable state.
Export documents in PDF, DOCX, HTML, and TXT so reviewers can circulate, mark up, and finish the work outside the workspace.
The workflow starts before writing. Teams need to define scope, map obligations, draft artifacts, capture evidence expectations, review gaps, and export a package that can survive scrutiny.
Start with the framework, regulation, audit request, policy area, product area, business unit, or customer questionnaire that drives the documentation need.
Turn obligations and reviewer expectations into a checklist, evidence matrix, working paper, filing support note, policy draft, or custom artifact.
Use prior documents, templates, policies, spreadsheets, exhibits, and source files where available so the draft reflects the organization's actual documentation base.
Use placeholders and reviewer notes to surface missing evidence, unconfirmed dates, owner notes, and unresolved assertions. Reviewers verify that the final artifact is complete.
Use comments, review state, assignees, due dates, versions, and edits to move the artifact toward a reviewer-ready package.
Export the package for audit, governance, legal, or customer review, then use your operational systems and professional reviewers to maintain the real-world compliance program.
Prepare checklists, evidence matrices, working papers, filing support notes, and policy drafts designed to surface missing facts as review items. Reviewers verify every fact and conclusion.
Lex exposes compliance forms and execution modes, so the team can choose a document shape and execution mode that matches the task.
Bring existing policies, templates, audit requests, customer documents, and supporting files into the drafting workflow.
Unsupported facts stay visible as gaps, placeholders, or reviewer notes. That is especially important for regulated documentation.
Use evidence matrices, risk registers, working papers, and checklist structures when a narrative document is not enough.
Comments, versions, assignees, due dates, and review state stay attached to the same artifact, and each export is written to an audit log (who exported it, the format, and whether it succeeded) rather than stored with the artifact.
Gixo helps prepare regulated work for review. Final judgment, filing, attestation, and signoff remain with qualified people and systems.
The compliance flow offers 20 forms across the five artifact families above. Three things decide how much review work a draft leaves.
Attach up to 20 evidence files to a compliance draft: PDF, Word, Excel, CSV, PowerPoint, scans and pictures (read by OCR), audio and video (transcribed). A scanned policy, a photographed register or a recorded walkthrough can sit beside the spreadsheets and PDFs it explains.
Figures in the draft are checked against the evidence you attached before your reviewer sees it, so a number the evidence does not carry is a question for the reviewer rather than a settled fact. Missing evidence stays an open item.
Compliance drafts built on a supported framework clause contract are checked clause by clause against a 80% coverage floor, and any shortfall is flagged for review (supported today: GDPR Article 30 records of processing, GDPR Article 30(2) processor records of processing, GDPR Article 35 data protection impact assessment, GDPR Articles 33 and 34 breach procedure and register, CCPA and CPRA notice at collection, HIPAA Notice of Privacy Practices, HIPAA Security Rule risk analysis). Other frameworks are drafted from your scope notes and evidence and reviewed by your team.
Gixo still does not collect evidence from your tools, test controls or issue signoff. For records of processing, see GDPR compliance documentation in Lex; for report narratives, see compliance reporting software.
Compliance audit software, risk and compliance software, compliance and risk management, financial services compliance software — these searches usually come from someone with an audit date in the calendar. The gap they are trying to close is almost never "we have no controls"; it is "the written evidence is scattered across four people and three years of drafts."
That is the part this drafts: control narratives, policy documents, risk artefacts and the records an assessor asks to see, structured against the framework you name, with the source material you supplied as reference input. For financial services specifically, SOX control documentation can use the general Control Document form, but there is no built-in SOX model: like every regime except GDPR Article 30 records of processing, GDPR Article 30(2) processor records of processing, GDPR Article 35 data protection impact assessment, GDPR Articles 33 and 34 breach procedure and register, CCPA and CPRA notice at collection, HIPAA Notice of Privacy Practices, HIPAA Security Rule risk analysis, SOX goes through the custom path, with the framework knowledge coming from the model's general understanding and from the scope notes and files you supply. What it does not do is run the audit, score your controls, or tell you that you passed — a qualified reviewer does that, and the draft exists to make their job shorter rather than to replace it.
People searching for compliance management software, risk and compliance software or governance risk and compliance software are usually looking for one of two different products. One monitors controls continuously; the other produces the written artefacts an assessor asks for. Gixo Lex is the second. It drafts the documentation against a named framework and leaves the monitoring to the platform you already run.
SOC 2 policies and control narratives, ISO 27001 Statement of Applicability sections and Annex A control narratives, and NIST-aligned documentation, drafted from the model's understanding of each framework and your scope notes and files rather than a built-in control catalog. SOC 2 checklist drafts · ISO 27001 documentation drafts
GDPR records of processing and DPIAs, and CCPA disclosures. The GDPR Article 30 record structure is modelled explicitly rather than approximated. GDPR document generator
HIPAA policies and risk artefacts, and PCI DSS documentation. If you searched for HIPAA compliance software or PCI compliance software expecting a scanner, this is the drafting half of that job. HIPAA drafts
SOX control documentation and the narratives that sit behind it, prepared for reviewer sign-off. What governance, risk and compliance means · What is a data retention policy
Those eight — SOC 2, ISO 27001, NIST, GDPR, CCPA, HIPAA, PCI DSS and SOX — can all be drafted as documentation, but built-in framework structures today cover only GDPR Article 30 records of processing, GDPR Article 30(2) processor records of processing, GDPR Article 35 data protection impact assessment, GDPR Articles 33 and 34 breach procedure and register, CCPA and CPRA notice at collection, HIPAA Notice of Privacy Practices, HIPAA Security Rule risk analysis, which Lex models clause by clause. Everything else goes through the custom document path, as does any framework outside that list: you name the framework and supply the requirement and the source material, and the draft is structured against what you provide, drawing on the model's general understanding of the framework rather than a built-in model or control catalog. That is how the long tail of sector-specific regimes gets covered without Gixo claiming sector expertise it does not have — the framework knowledge comes from the model and from you, the drafting structure and the review pass come from the product. Alongside the compliance work sit 29 named legal document types across confidentiality and IP, services and commerce, corporate and equity, employment, real estate and finance. Every output is a reviewable draft for a qualified reviewer to check; Gixo does not certify compliance and does not monitor your controls.
The job is not to ask AI for a legal answer. The job is to prepare a draft or artifact that a qualified reviewer can actually work with.
| Capability | Gixo Lex | Spreadsheets and docs | GRC platforms | General AI chat |
|---|---|---|---|---|
| Main job | Draft reviewable compliance artifacts | Manual documentation | Operational compliance system | Prompt output |
| Artifact types | Checklists, evidence matrices, working papers, filing notes, policy drafts | Any, but manual | Reports and dashboards | Unstructured unless prompted |
| Evidence mapping | Structured in the draft | Manual | Often automated | Paste-only |
| Missing-info handling | Open gaps stay visible | Manual discipline | Depends on configuration | Risk of overconfident text |
| Control-system surveillance | Not included | No | Often included | No |
| Reviewer-ready export | PDF, DOCX, HTML, TXT | Manual cleanup | Reports and exports | Manual copy/paste |
| Compliance attestation | Not included | Ask the vendor | Still requires review | Ask the vendor |
The other columns describe what each kind of tool is generally for, not a test of a named product, and products differ. Run the same brief and reference files through anything on your shortlist, then compare the draft, the review trail and the export.
"Compliance software" covers at least four distinct jobs, and buying the wrong one is the usual reason a purchase disappoints. Naming them makes the choice easier — including the cases where the answer is not Gixo.
Compliance management software runs the ongoing programme: control libraries, owners, assessment cycles, issues, exceptions and reporting. This is the operational system of record, and it is what most people mean when they search for compliance management as a product category. Gixo Lex is not this, and does not try to be.
Compliance audit software and audit software more broadly connect to live systems, gather evidence on a schedule and track findings through to closure. Drata, Vanta, Sprinto and Secureframe sit here. If your problem is that evidence collection is manual and repetitive, that is the category to buy, not a drafting workspace.
Some buyers need a framework-shaped product rather than a general one — HIPAA compliance software for covered entities and business associates, PCI compliance software for cardholder-data environments, or a SOC 2 or ISO 27001 readiness tool. These narrow the control set and the evidence model to one regime, which is genuinely useful when you only have one regime to satisfy.
Operational platforms can also provide policy templates, AI drafting and document review. The buyer decision is which drafting, review and operational controls the current product provides for your actual artifact. That is the layer Gixo Lex works on: it turns the facts and reference files you supply into reviewable first drafts, and leaves the missing facts visible as open items rather than filling them in. It is a drafting and review workspace, not a monitoring platform.
Teams get better results when they start with one reviewable documentation workflow, then expand only after the artifact standards are clear.
Pick one recurring document, such as a checklist, evidence matrix, policy draft, or working paper, and define the required sections, evidence fields, and gap rules.
Bring in templates, prior period documents, customer requests, and source material, then attach comments, assignees, and due dates to the same artifact.
Connect related artifacts such as risk registers, evidence matrices, working papers, policy drafts, and filing support notes so reviewers can trace the story across the package.
Compliance documents should preserve scope, source, reviewer, and update context so the next review does not restart from zero.
A beautiful artifact is not useful if it buries missing support. Gaps need to remain visible until a human resolves them.
Draft preparation is not control surveillance, evidence collection, legal advice, or compliance attestation. Keep those boundaries explicit.
Official information checked 10 October 2026: Vanta describes policy and questionnaire drafting; Drata describes policy creation, review, approval and AI control mapping; Secureframe describes policy editing, AI revisions and acceptance tracking. ISMS Copilot describes policy drafts, risk assessments, control mapping and audit preparation, without collecting live operational evidence or monitoring running controls. These vendor statements do not prove a particular plan or output quality. Compare one safe policy or evidence-matrix job, source handling, review controls and the exported artifact.
Lex prepares the document for qualified review. It does not collect operational evidence, test controls continuously or certify compliance; assess those requirements separately even when one vendor offers both jobs.
Updated