
Make the intake specific
Supply the parties, document kind, jurisdiction, obligations, dates and reference material. Review imported content and retain its source identity before using it in a new matter.
Use Gixo for DPIAs, Article 30 records, rights procedures, breach-response drafts, and transfer assessments when the team needs GDPR-oriented structure with visible review and open items.
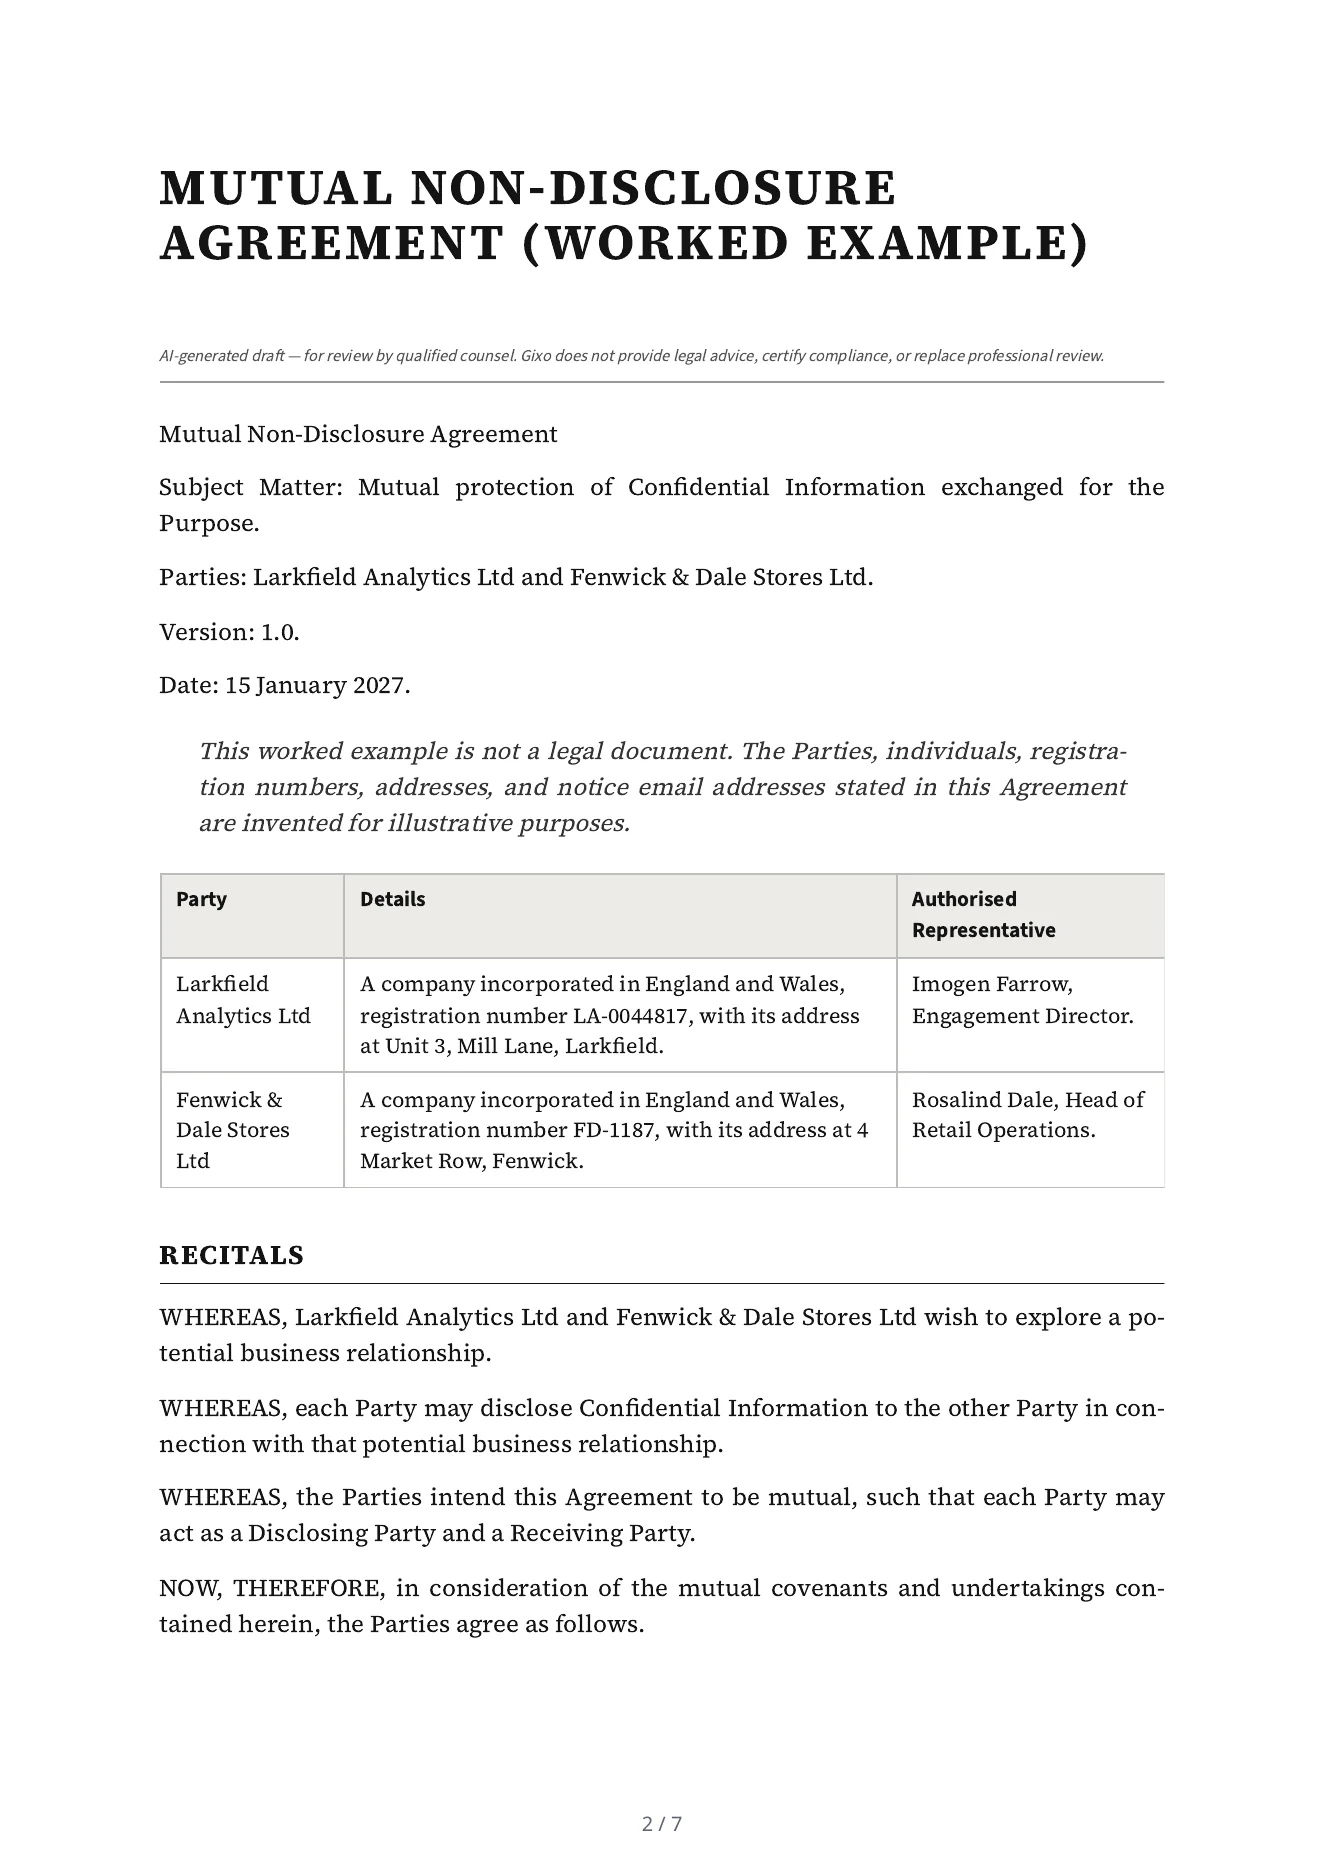
This is a real Lex export for invented parties. Inspect the input and clauses as a worked example, with professional review kept separate from automated drafting and checks.
A mutual non-disclosure agreement of 14 numbered clauses between two invented parties: definitions, what counts as confidential information, exclusions, the receiving party's obligations, permitted disclosures, return of materials, remedies, term, survival, governing law, notices and signature blocks. Its first page says it is a worked example, not a legal document.
Draft a Mutual Non-Disclosure Agreement between Larkfield Analytics Ltd (Party A) and Fenwick & Dale Stores Ltd (Party B). Governing law: England and Wales. Effective date: 2027-01-15. Term: Two years from the effective date. Confidentiality: Three years after disclosure. A mutual agreement: each party may disclose and receive confidential information. State on the first page that the parties, people and addresses in this agreement are invented and that it is a worked example, not a legal document. The notice email address of Larkfield Analytics Ltd is notices@larkfield-analytics.example and of Fenwick & Dale Stores Ltd is notices@fenwick-dale.example (both invented).
Read mechanically against the intake, not by a lawyer: all 12 facts the intake gave are in the draft, nothing is left as a placeholder, and it states no term the intake did not give.
Supply the parties, document kind, jurisdiction, obligations, dates and reference material. Review imported content and retain its source identity before using it in a new matter.
Use the legal workspace's permitted structural tools, Draft Checks and review paths. Compare proposed changes with the saved draft and original material; unsupported Word edits must be handled explicitly.
Have qualified counsel review enforceability, local requirements and the actual commercial intent. Check the current approval state and the downloaded document after a change.
Select the target clause and give Ask Lex a bounded instruction. Missing facts remain visible for review. Inspect the before-and-after proposal, required clause checks and any explicit outside-matrix or mandatory-clause override before versioned application. Use the legal workspace's structural allowlist rather than assuming every general content-editor block is available.
Inspect immutable playbook versions, anchored findings, provenance and precedent variants before staging a change. Matters retain original sources, quotation findings and source-version comparisons. Review extracted obligations for timing, ownership and source revision; negotiation turns and agreement-pack review cells have their own decisions and current-version requirements.
Original-format Word export, tracked changes against an original and saved-version redlines are separate paths. Unsupported edits must be surfaced rather than silently claimed as preserved. Inspect the layout, validator notes and downloaded file, then retain its delivery receipt. Counsel's review applies to the actual matter and version.
Every contract in Lex, drafted or imported, gets an AI contract review: each clause the document type expects marked present, weak or absent; up to 25 risks with a level, the party each falls on, why it matters and replacement wording; and provisions that cannot both be followed. Every quotation is checked against the contract text, findings are decided before approval, and there is no single risk score. The same review reads the key terms and obligations with the words they quote and proposes them into the Agreement Pack. Review every document puts up to 25 documents of an Agreement Pack, or up to 200 in a matter, into one table with your own questions as columns and an Excel export. Approvers can be named in order, and signing supports up to 10 signers with an optional signing order and automatic reminders; it is a simple electronic signature, not a qualified one. A qualified reviewer still decides what the contract says.
Lex does not provide legal advice or certify compliance. The public specimen is not a universally reusable legal template. Word fidelity depends on the supported original-document and saved-version path; unrestricted Power Edit and image insertion are not legal editing features.
Gixo is an AI GDPR compliance document generator that drafts reviewable artifacts — DPIAs, Article 30 records of processing, data-subject rights procedures, transfer assessments, and breach-response documents — with GDPR-oriented structure and visible open items. It exports to PDF, DOCX, HTML, and TXT, keeps review, comments, and versions on the same document, and prepares work for professional review rather than certifying compliance.
Prepare compliance drafts designed to surface missing facts as review items. Reviewers still verify every fact and conclusion before action.
Prepare impact-assessment drafts with the processing description, risk analysis, and mitigation structure reviewers expect to see.
Generate records of processing, rights procedures, and related documentation with placeholders where the facts are not yet complete.
Reference files and governing context can shape the draft. Cited sources can show which draft sentences are supported by supplied reference files. This in-app support does not establish legal authority or statutory compliance and is not inserted into the contract or its exports; reviewers still check the facts and law independently.
Prepare transfer-assessment and breach-response artifacts without pretending the system replaces the operational privacy program or regulator workflow.
The workflow is designed to surface missing facts, unresolved decisions, and reviewer questions. Reviewers confirm the document is complete.
After the first draft, Lex runs an AI contract review of the whole contract, with every quotation checked against the text, beside rule checks: clause coverage against a versioned playbook, clause-conflict detection, and defined-term and cross-reference checks. Findings, tracked-change DOCX redlines, comments, review state, assignees, due dates, and version history all stay attached to the same document. A contract imported from Word can go back as that same DOCX, with the Lex edits shown as Word tracked changes; where Lex cannot track an edit faithfully, such as inside a field, an existing revision, a header or a footer, it refuses the export instead of altering the document. Reviewers still verify every clause and conclusion.
Start with the job: DPIA, processing record, rights procedure, transfer assessment, or breach-response support.
Bring in the processing purpose, systems, recipients, risks, or incident context that will shape the document.
Prepare the draft with GDPR-oriented sections, open items, and reviewer-visible assumptions.
Keep privacy, legal, and audit review on the same document, then export in PDF, DOCX, HTML, and TXT when it is ready for the next step.
Each of these is a draft artifact for reviewer handoff, not certified or filed compliance. Gixo does not run the operational privacy program, consent tooling, or regulator submission. Article 30 controller and processor records, Article 35 DPIAs, and Articles 33–34 breach-response documents run against built-in clause contracts that check each paragraph listed below explicitly, including a stated reason wherever one doesn't apply — the other document types below follow article structure without that per-paragraph coverage check.
| GDPR document | What Gixo drafts | Article reference use | Open items surfaced | Export |
|---|---|---|---|---|
| DPIA (Data Protection Impact Assessment) | Processing description, necessity/proportionality, risk analysis, mitigation sections | Art. 35(1)/(2)/(3)/(7)–(9) — every paragraph checked | Yes — explicit per-paragraph, not just missing facts | PDF, DOCX, HTML, and TXT |
| Article 30 Record of Processing (RoPA) | Purposes, categories, recipients, retention, transfer basis (controller & processor) | Art. 30(1)/(2)/(3)/(4)/(5) — every paragraph checked | Yes — explicit per-paragraph, not just missing facts | PDF, DOCX, HTML, and TXT |
| Data-subject rights procedure | Request intake, verification, response and timeline steps | Art. 12–22 structure | Yes | PDF, DOCX, HTML, and TXT |
| International transfer assessment | Transfer mechanism, risk factors, supplementary measures | Ch. V structure | Yes | PDF, DOCX, HTML, and TXT |
| Breach-response document | Incident facts, risk-to-rights assessment, notification support, internal register | Art. 33(1)–(5) & 34(1)–(4) — every paragraph checked | Yes — explicit per-paragraph, not just missing facts | PDF, DOCX, HTML, and TXT |
| Capability | Gixo | Consent platforms | Privacy ops tools | Manual documents |
|---|---|---|---|---|
| Main job | GDPR artifact drafting | Cookie and consent workflow | Operational privacy program | Manual |
| DPIA and record drafting | Yes | Test on the same inputs | Ask the vendor | Manual |
| GDPR-oriented written artifact | Structured draft; reviewer verification required | Ask the vendor | Ask the vendor | Manual |
| Direct regulator workflow | Not included | No | No | External |
| Review workflow on the document | Yes | Ask the vendor | Ask the vendor | No |
The other columns describe what each kind of tool is generally for, not a test of a named product, and products differ. Ask whether it produces a DPIA or Article 30 draft you can export, and where a reviewer marks open items. Run the same brief and reference files through anything on your shortlist, then compare the draft, the review trail and the export.
Updated