
Make the intake specific
Supply the parties, document kind, jurisdiction, obligations, dates and reference material. Review imported content and retain its source identity before using it in a new matter.
Start with a named framework or your own structure. Gixo prepares a reviewable checklist draft with evidence fields, status placeholders, and gap notes instead of pretending your monitoring data already exists.
An AI compliance checklist generator is a tool that turns a named framework or your own structure into a reviewable checklist draft — with evidence fields, status placeholders, and gap notes — instead of a finished audit. Gixo's version drafts from a brief or prior file, lets you harmonize one checklist across multiple jurisdictions by mapping each control to the strictest applicable requirement, and exports as PDF, DOCX, HTML, or TXT. It prepares the artifact for reviewers; it does not automate evidence collection or provide always-on platform monitoring.
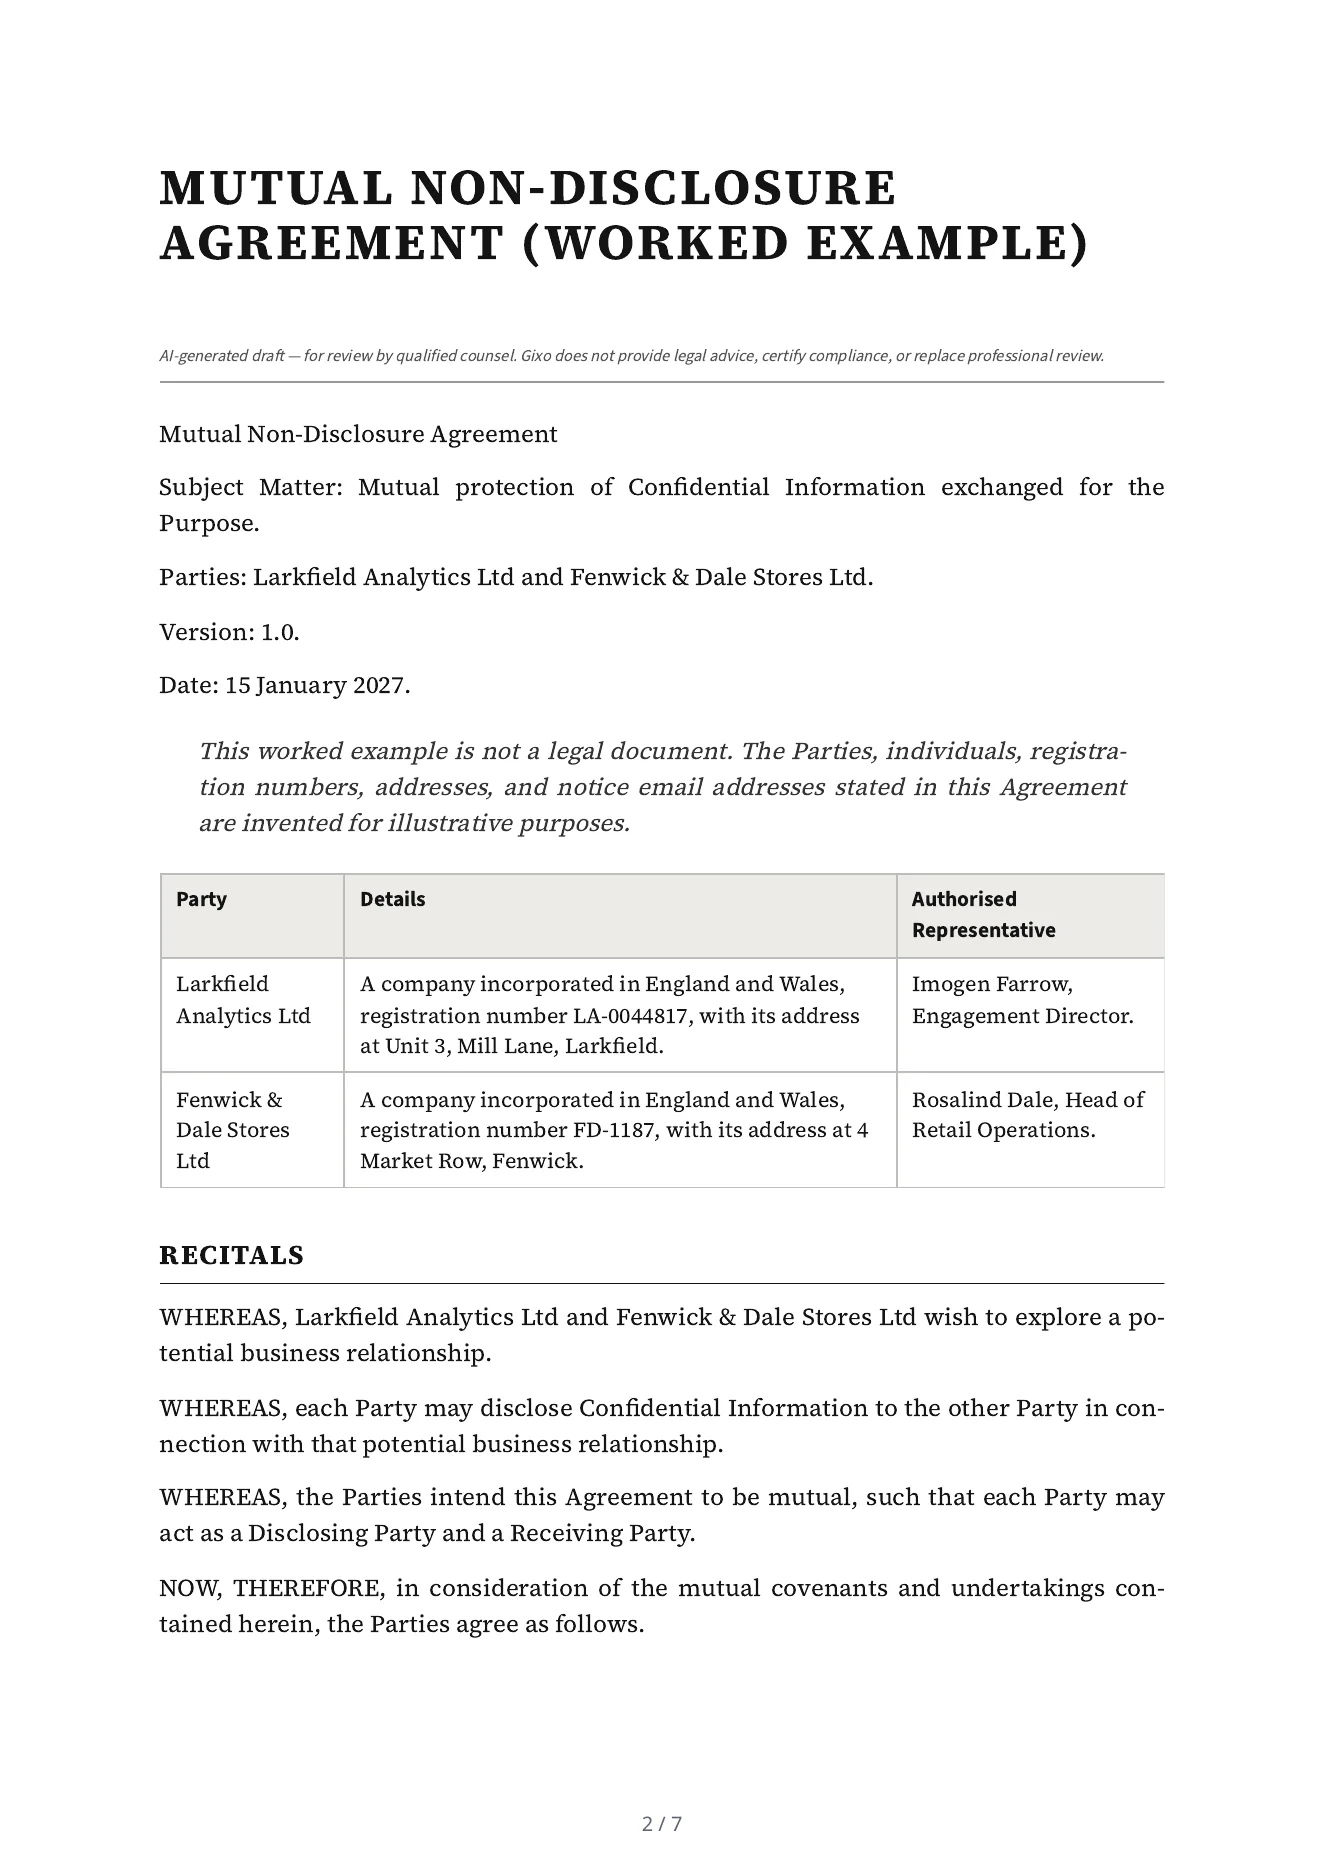
This is a real Lex export for invented parties. Inspect the input and clauses as a worked example, with professional review kept separate from automated drafting and checks.
A mutual non-disclosure agreement of 14 numbered clauses between two invented parties: definitions, what counts as confidential information, exclusions, the receiving party's obligations, permitted disclosures, return of materials, remedies, term, survival, governing law, notices and signature blocks. Its first page says it is a worked example, not a legal document.
Draft a Mutual Non-Disclosure Agreement between Larkfield Analytics Ltd (Party A) and Fenwick & Dale Stores Ltd (Party B). Governing law: England and Wales. Effective date: 2027-01-15. Term: Two years from the effective date. Confidentiality: Three years after disclosure. A mutual agreement: each party may disclose and receive confidential information. State on the first page that the parties, people and addresses in this agreement are invented and that it is a worked example, not a legal document. The notice email address of Larkfield Analytics Ltd is notices@larkfield-analytics.example and of Fenwick & Dale Stores Ltd is notices@fenwick-dale.example (both invented).
Read mechanically against the intake, not by a lawyer: all 12 facts the intake gave are in the draft, nothing is left as a placeholder, and it states no term the intake did not give.
Supply the parties, document kind, jurisdiction, obligations, dates and reference material. Review imported content and retain its source identity before using it in a new matter.
Use the legal workspace's permitted structural tools, Draft Checks and review paths. Compare proposed changes with the saved draft and original material; unsupported Word edits must be handled explicitly.
Have qualified counsel review enforceability, local requirements and the actual commercial intent. Check the current approval state and the downloaded document after a change.
Select the target clause and give Ask Lex a bounded instruction. Missing facts remain visible for review. Inspect the before-and-after proposal, required clause checks and any explicit outside-matrix or mandatory-clause override before versioned application. Use the legal workspace's structural allowlist rather than assuming every general content-editor block is available.
Inspect immutable playbook versions, anchored findings, provenance and precedent variants before staging a change. Matters retain original sources, quotation findings and source-version comparisons. Review extracted obligations for timing, ownership and source revision; negotiation turns and agreement-pack review cells have their own decisions and current-version requirements.
Original-format Word export, tracked changes against an original and saved-version redlines are separate paths. Unsupported edits must be surfaced rather than silently claimed as preserved. Inspect the layout, validator notes and downloaded file, then retain its delivery receipt. Counsel's review applies to the actual matter and version.
Every contract in Lex, drafted or imported, gets an AI contract review: each clause the document type expects marked present, weak or absent; up to 25 risks with a level, the party each falls on, why it matters and replacement wording; and provisions that cannot both be followed. Every quotation is checked against the contract text, findings are decided before approval, and there is no single risk score. The same review reads the key terms and obligations with the words they quote and proposes them into the Agreement Pack. Review every document puts up to 25 documents of an Agreement Pack, or up to 200 in a matter, into one table with your own questions as columns and an Excel export. Approvers can be named in order, and signing supports up to 10 signers with an optional signing order and automatic reminders; it is a simple electronic signature, not a qualified one. A qualified reviewer still decides what the contract says.
Lex does not provide legal advice or certify compliance. The public specimen is not a universally reusable legal template. Word fidelity depends on the supported original-document and saved-version path; unrestricted Power Edit and image insertion are not legal editing features.
Try a prepared Lex task
Turn a fictional internal policy into requirements, evidence fields and open review items. This example tests a checklist workflow; it does not establish statutory compliance or legal validity.
Fictional, hand-authored example. The source and preview below are illustrative; they are not customer work, a generated result, or an approved deliverable.
FICTIONAL INTERNAL POLICY — these are supplied requirements, not a law or standard.
Entity: Harbor Studio, a fictional six-person design agency.
Requirement R1: keep a named owner for each shared project folder.
Requirement R2: the owner reviews the active access list at the end of each project.
Requirement R3: record any access removal request and who confirmed completion.
Requirement R4: unresolved access questions go to the operations lead for review.
Evidence supplied: none. Access lists, review dates and removal receipts must remain missing/open.
Scope: a review exercise for one fictional project. Jurisdiction and legal applicability have not been established.
Keep every control Open and every evidence item missing, and leave certification to the reviewer.
Evidence needed: folder ownership record. Status: Open — no evidence supplied. Reviewer action: confirm the responsible owner before evaluating access.
Evidence needed: removal request and completion receipt. Status: Open — no evidence supplied. Reviewer action: check the recorded request against the actual access list.
The example loads the input; you choose when to plan or generate. Current sign-in, product access, usage and export requirements apply. Review any output before use.
Start with a named framework or a custom structure. Gixo prepares a checklist draft with evidence fields, status placeholders, and room to mark open items instead of guessing.
Name the framework or define a custom structure. Gixo shapes a checklist draft around the clauses or control groups your team wants to review; outside GDPR Article 30 records of processing, GDPR Article 30(2) processor records of processing, GDPR Article 35 data protection impact assessment, GDPR Articles 33 and 34 breach procedure and register, CCPA and CPRA notice at collection, HIPAA Notice of Privacy Practices, HIPAA Security Rule risk analysis, that framing comes from the model's understanding of the framework rather than a built-in control catalog.
Each line can include evidence expectations and support notes so the reviewer sees what still needs to be attached or confirmed.
Mark items as complete, in progress, needs review, or missing evidence in the draft itself. This is artifact prep, not a live monitoring system.
Capture the team, function, or reviewer responsible for follow-up in the checklist text. Gixo does not replace a dedicated control-ownership platform.
Add review frequency, open questions, or next-review notes where needed so the exported checklist is easier for a manager, auditor, or counsel to work through.
Missing facts stay visible as open items or placeholder notes instead of being invented by the model.
Start from a named framework or define your own structure for the review job in front of your team.
Each section can include evidence notes, status placeholders, and support text so reviewers see what still needs confirmation.
Capture open items, responsible teams, or reviewer notes inside the draft without pretending the operational workflow already exists.
Export the checklist as a reviewable PDF, DOCX, HTML, or TXT artifact your team can circulate, comment on, and finish.
Evaluate the job boundary and the evidence you can inspect. A checklist-drafting workspace, an operational monitoring system, and a manual document process solve different parts of compliance work.
Confirm that framework structure, evidence fields, responsibility notes, and unresolved inputs remain visible in the exported checklist.
Decide whether the current bottleneck is preparing reviewable documentation or operating continuous evidence collection and control monitoring. Gixo addresses the drafting layer, not the latter.
Use the same safe brief and prior file, then compare missing-information handling, reviewer effort, and export quality against your written requirements.
Choose requirements before choosing software. A document workspace should be tested for framework structure, visible gaps, reviewer effort, version history, and export quality. An operational monitoring system should be tested separately for evidence collection, integrations, control ownership, alerting, and continuous status. If both jobs matter, verify the handoff between them with your own workflow.
The scalable way to handle multiple regimes is not a separate checklist per country — it is one harmonized set of controls built to the strictest applicable requirement, then mapped back to each law. That is what keeps a cross-jurisdiction checklist defensible instead of a documentation nightmare.
Pull the specific obligations from each regime that applies to you — data protection, security, sector rules — across every jurisdiction you operate in.
Where two regimes overlap, write one control that satisfies the tougher one. For example, if one regime expects breach notification within 72 hours and another is less specific, set 72 hours for everyone.
Add the article, clause, or framework reference reviewers expect each checklist item to address, so one harmonized line can carry GDPR, CCPA, SOC 2, and ISO 27001 at once instead of four parallel checklists. The checklist workflow does not validate that mapping, so qualified reviewers confirm every requirement link against current source material.
Naming the framework changes the spine of the checklist — what the items are grouped by, what counts as evidence for a line, and what a reviewer is entitled to conclude at the end. Gixo shapes the draft around the framework you name and the source material you supply. Apart from the clause contracts Lex carries (GDPR Article 30 records of processing, GDPR Article 30(2) processor records of processing, GDPR Article 35 data protection impact assessment, GDPR Articles 33 and 34 breach procedure and register, CCPA and CPRA notice at collection, HIPAA Notice of Privacy Practices, HIPAA Security Rule risk analysis), it does not carry a built-in framework model or control library for these regimes, does not assess your controls against them, and does not attest to the outcome.
A GDPR compliance checklist is organised by article and by processing activity rather than by security control. The recurring lines are the lawful basis for each activity (Article 6, and Article 9 where special-category data is involved), the record of processing activities under Article 30, data-subject request handling inside the one-month window in Article 12(3), a DPIA where processing is likely to be high risk under Article 35, Article 28 terms for every processor, a named transfer mechanism per non-EEA recipient under Chapter V, and the 72-hour supervisory-authority notification clock in Article 33.
GDPR is where Lex models the most artifacts clause by clause. The GDPR Article 30 record of processing, for example, is registered as a clause contract, so statutory mode walks 30(1)(a) through 30(1)(f) in order, keeps a structured recipient-categories table, and forces an explicit conclusion on international transfers — Not Applicable — no international transfers is recorded as an answer rather than left as a silent gap. A framework on this page with no contract in that list, such as PCI DSS, ISO 27001, CMMC or DORA, runs through the custom path instead. Deeper GDPR artifacts live on the GDPR document generator.
A HIPAA compliance checklist has to span three rules, not one: the Privacy Rule, the Security Rule, and the Breach Notification Rule. The Security Rule then splits again into administrative, physical, and technical safeguards. The detail most checklists get wrong is that its implementation specifications come in two kinds — required and addressable — and addressable does not mean optional. If you do not implement an addressable specification you are expected to document why it was not reasonable and appropriate for you and what equivalent measure you put in place instead.
That is why a HIPAA checklist needs a justification field next to the status column, not just a tick box, and why the risk analysis and the business associate agreement register usually become their own sections. Gixo drafts the checklist and the written justification prose around the facts you supply; it does not perform the risk analysis, and there is no HHS certificate at the end of it — see what HIPAA compliance actually means.
A PCI DSS compliance checklist is built on the 12 requirements grouped under six control objectives, but the useful work happens before the checklist does: scope. What sits inside the cardholder data environment decides how many of those requirements apply, and the validation route decides how the checklist is written up — a self-assessment questionnaire whose type (A, A-EP, B, B-IP, C, C-VT, P2PE or D) reflects how you handle card data, or a Report on Compliance prepared by a qualified security assessor at higher merchant levels.
Version 4.x also added a customised approach alongside the defined approach, so a requirement can now be satisfied by a documented alternative control supported by a targeted risk analysis. That is drafting work, and it is where a checklist generator earns its place: Gixo prepares the requirement list, the scope notes, and the customised-approach narrative for review. It does not scan the cardholder data environment, and it does not sign an attestation of compliance.
Most ISO 27001 compliance checklists cover half the standard. Clauses 4 to 10 — context, leadership, planning, support, operation, performance evaluation, and improvement — are the management-system requirements, and they are the part an auditor certifies against. Annex A is a reference set of controls, 93 of them across organisational, people, physical, and technological themes in the 2022 revision, and each one is included or excluded with a justification recorded in the Statement of Applicability. A checklist that lists Annex A controls and stops has skipped the clauses.
Gixo can shape a checklist across both halves. Like every framework here except GDPR Article 30 records of processing, GDPR Article 30(2) processor records of processing, GDPR Article 35 data protection impact assessment, GDPR Articles 33 and 34 breach procedure and register, CCPA and CPRA notice at collection, HIPAA Notice of Privacy Practices, HIPAA Security Rule risk analysis, ISO 27001 runs through the custom path, so the clause and Annex A structure comes from the model's understanding of the standard and the scope notes and files you supply, not a built-in Annex A catalog. Statement of Applicability sections and Annex A control narratives are drafted in that same compliance flow rather than a separate tool; the ISO 27001 documentation drafts page covers how to scope them. Certification itself comes from an accredited certification body after a Stage 1 and Stage 2 audit — no drafting tool issues it.
A CMMC compliance checklist starts by settling the level, because the practice set changes completely between them. Level 1 covers basic safeguarding of Federal Contract Information and is self-assessed with an annual affirmation. Level 2 is built on the requirements of NIST SP 800-171 for Controlled Unclassified Information, assessed either by self-assessment or by a certified third-party assessment organisation depending on the contract. Level 3 layers on selected NIST SP 800-172 requirements with government-led assessment.
The two documents that actually get read are the System Security Plan and the Plan of Action and Milestones, so a CMMC checklist is mostly a scoring and evidence map that feeds those two artifacts. Lex models only GDPR Article 30 records of processing, GDPR Article 30(2) processor records of processing, GDPR Article 35 data protection impact assessment, GDPR Articles 33 and 34 breach procedure and register, CCPA and CPRA notice at collection, HIPAA Notice of Privacy Practices, HIPAA Security Rule risk analysis explicitly, so CMMC runs through the custom path, where you supply the practice list and the source text and Gixo structures the checklist and the supporting narrative around what you provided. Phase-in dates and rule text move; confirm the current position against official Department of Defense sources before relying on any draft.
DORA — the EU Digital Operational Resilience Act, Regulation (EU) 2022/2554 — has applied to EU financial entities and their critical ICT service providers since 17 January 2025. A DORA compliance checklist follows its five pillars: ICT risk management, incident classification and reporting, digital operational resilience testing including threat-led penetration testing for the entities in scope for it, ICT third-party risk, and information sharing.
What makes a DORA checklist unlike a security-control checklist is the Register of Information: a structured inventory of every contractual arrangement with an ICT third-party provider, maintained and reported to your competent authority. That pushes the work toward contracts, registers, and exit arrangements rather than technical controls alone. Like CMMC, DORA runs through the custom path — Gixo structures the checklist and the register-supporting narrative from the obligations and contract facts you supply, and a qualified reviewer confirms the mapping against the current regulation and the relevant regulatory technical standards.
The most expensive misunderstanding in compliance tooling is assuming the thing that produces the checklist can also close it. In every row below, Gixo prepares the draft for review. None of these outcomes are issued by Gixo, and completing a checklist in the workspace does not create one.
| Framework | What the checklist is organised around | What the formal outcome is, and who issues it |
|---|---|---|
| GDPR | Articles and processing activities: lawful basis, Article 30 records, data-subject requests, DPIAs, transfer mechanisms, the 72-hour breach clock | No general certificate. The checklist is read by your DPO, by a supervisory authority on request, or by a customer's due-diligence reviewer |
| HIPAA | Privacy, Security, and Breach Notification rules, with Security Rule specifications split into required and addressable | No government certification exists. Covered entities and business associates document their own position; OCR reviews it on investigation |
| PCI DSS | 12 requirements applied to whatever sits inside the cardholder data environment, scoped by SAQ type | An attestation of compliance after self-assessment, or a Report on Compliance written by a qualified security assessor |
| ISO 27001 | Clauses 4 to 10 as the management system, plus the Annex A controls you include or exclude in the Statement of Applicability | A certificate issued by an accredited certification body after a Stage 1 and Stage 2 audit |
| CMMC | The practice set for your level: basic safeguarding at Level 1, NIST SP 800-171 at Level 2, selected NIST SP 800-172 requirements at Level 3 | A self-assessment with affirmation, a certified third-party assessment, or a government-led assessment, depending on level and contract |
| DORA | Five pillars plus the Register of Information covering every ICT third-party contractual arrangement | No certificate. Your competent authority supervises directly, and the register is reported to it |
Regulatory examples on this page are illustrative and change over time — confirm current requirements with qualified legal counsel. Gixo helps prepare regulated work. It does not provide legal advice, certify compliance, or replace professional review.
Updated